An amendment numbered 7 printed in House Report 111-419 to require the President to submit detailed notifications to Congress on current and newly-created cybersecurity programs.
What it does: Adds SEC. 355. CYBERSECURITY OVERSIGHT after section 354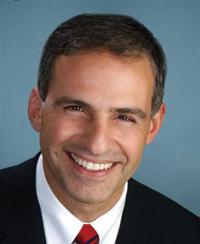 Rep. Michael A. Arcuri (D-NY)
Description
Amendment requires the President to submit detailed notifications to Congress on current and newly-created cybersecurity programs.
What it changes
1 change to H.R. 2701
We couldn't match these changes to the text of H.R. 2701, so they're shown as written.
Adds SEC. 355. CYBERSECURITY OVERSIGHT after section 354
Adds a sectionInserted: SEC. 355. CYBERSECURITY OVERSIGHT.
Inserted: (a) Notification of Cybersecurity Programs.--
Inserted: (1) Requirement for notification.--
Inserted: (A) Existing programs.--Not later than 30 days after the date of the enactment of this Act, the President shall submit to Congress a notification for each cybersecurity program in operation on such date that includes the documentation referred to in subparagraphs (A) through (E) of paragraph (2).
Inserted: (B) New programs.--Not later than 30 days after the date of the commencement of operations of a new cybersecurity program, the President shall submit to Congress a notification of such commencement that includes the documentation referred to in subparagraphs (A) through (E) of paragraph (2).
Inserted: (2) Documentation.--A notification required by paragraph (1) for a cybersecurity program shall include--
Inserted: (A) the legal justification for the cybersecurity program;
Inserted: (B) the certification, if any, made pursuant to section 2511(2)(a)(ii)(B) of title 18, United States Code, or other statutory certification of legality for the cybersecurity program;
Inserted: (C) the concept for the operation of the cybersecurity program that is approved by the head of the appropriate agency or department;
Inserted: (D) the assessment, if any, of the privacy impact of the cybersecurity program prepared by the privacy or civil liberties protection officer or comparable officer of such agency or department; and
Inserted: (E) the plan, if any, for independent audit or review of the cybersecurity program to be carried out by the head of the relevant department or agency of the United States, in conjunction with the appropriate inspector general.
Inserted: (b) Program Reports.--
Show 33 more inserted paragraphsShow less
Inserted: (1) Requirement for reports.--The head of a department or agency of the United States with responsibility for a cybersecurity program for which a notification was submitted under subsection (a), in consultation with the inspector general for that department or agency, shall submit to Congress and the President, in accordance with the schedule set out in paragraph (2), a report on such cybersecurity program that includes--
Inserted: (A) the results of any audit or review of the cybersecurity program carried out under the plan referred to in subsection (a)(2)(E), if any; and
Inserted: (B) an assessment of whether the implementation of the cybersecurity program--
Inserted: (i) is in compliance with--
Inserted: (I) the legal justification referred to in subsection (a)(2)(A); and
Inserted: (II) the assessment referred to in subsection (a)(2)(D), if any;
Inserted: (ii) is adequately described by the concept of operation referred to in subsection (a)(2)(C), if any; and
Inserted: (iii) includes an adequate independent audit or review system and whether improvements to such independent audit or review system are necessary.
Inserted: (2) Schedule for submission of reports.--The reports required by paragraph (1) shall be submitted to Congress and the President according to the following schedule:
Inserted: (A) An initial report shall be submitted not later than 180 days after the date of the enactment of this Act.
Inserted: (B) A second report shall be submitted not later than one year after the date of the enactment of this Act.
Inserted: (C) Additional reports shall be submitted periodically following the submission of the reports referred to in subparagraphs (A) and (B) as necessary, as determined by the head of the relevant department or agency of the United States in conjunction with the inspector general of that department or agency.
Inserted: (3) Cooperation and coordination.--
Inserted: (A) Cooperation.--The head of each department or agency of the United States required to submit a report under paragraph (1) for a particular cybersecurity program, and the inspector general of each such department or agency, shall, to the extent practicable, work in conjunction with any other such head or inspector general required to submit such a report for such cybersecurity program.
Inserted: (B) Coordination.--The heads of all of the departments and agencies of the United States required to submit a report under paragraph (1) for a particular cybersecurity program shall designate one such head to coordinate the conduct of the reports on such program.
Inserted: (c) Information Sharing Report.--Not later than one year after the date of the enactment of this Act, the Inspector General of the Department of Homeland Security and the Inspector General of the Intelligence Community shall jointly submit to Congress and the President a report on the status of the sharing of cyber threat information, including--
Inserted: (1) a description of how cyber threat intelligence information, including classified information, is shared among the agencies and departments of the United States and with persons responsible for critical infrastructure;
Inserted: (2) a description of the mechanisms by which classified cyber threat information is distributed;
Inserted: (3) an assessment of the effectiveness of such information sharing and distribution; and
Inserted: (4) any other matters identified by the Inspectors General that would help to fully inform Congress or the President regarding the effectiveness and legality of cybersecurity programs.
Inserted: (d) Personnel Details.--
Inserted: (1) Authority to detail.--Notwithstanding any other provision of law, the head of an element of the intelligence community that is funded through the National Intelligence Program may detail an officer or employee of such element to the National Cyber Investigative Joint Task Force or to the Department of Homeland Security to assist the Task Force or the Department with cybersecurity, as jointly agreed by the head of such element and the Task Force or the Department.
Inserted: (2) Basis for detail.--A personnel detail made under paragraph (1) may be made--
Inserted: (A) for a period of not more than three years; and
Inserted: (B) on a reimbursable or nonreimbursable basis.
Inserted: (e) Sunset.--The requirements and authorities of this section shall terminate on December 31, 2012.
Inserted: (f) Definitions.--In this section:
Inserted: (1) Cybersecurity program.--The term "cybersecurity program" means a class or collection of similar cybersecurity operations of an agency or department of the United States that involves personally identifiable data that is--
Inserted: (A) screened by a cybersecurity system outside of the agency or department of the United States that was the intended recipient of the personally identifiable data;
Inserted: (B) transferred, for the purpose of cybersecurity, outside the agency or department of the United States that was the intended recipient of the personally identifiable data; or
Inserted: (C) transferred, for the purpose of cybersecurity, to an element of the intelligence community.
Inserted: (2) National cyber investigative joint task force.--The term "National Cyber Investigative Joint Task Force" means the multi-agency cyber investigation coordination organization overseen by the Director of the Federal Bureau of Investigation known as the Nation Cyber Investigative Joint Task Force that coordinates, integrates, and provides pertinent information related to cybersecurity investigations.
Inserted: (3) Critical infrastructure.--The term "critical infrastructure" has the meaning given that term in section 1016 of the USA PATRIOT Act (42 U.S.C. 5195c).
Original wording
Insert after section 354 the following new section:
Read automatically from the Congressional Record. Check the original before relying on it.
As printed
Insert after section 354 the following new section:
SEC. 355. CYBERSECURITY OVERSIGHT.
(a) Notification of Cybersecurity Programs.--
(1) Requirement for notification.--
(A) Existing programs.--Not later than 30 days after the date of the enactment of this Act, the President shall submit to Congress a notification for each cybersecurity program in operation on such date that includes the documentation referred to in subparagraphs (A) through (E) of paragraph (2).
(B) New programs.--Not later than 30 days after the date of the commencement of operations of a new cybersecurity program, the President shall submit to Congress a notification of such commencement that includes the documentation referred to in subparagraphs (A) through (E) of paragraph (2).
(2) Documentation.--A notification required by paragraph (1) for a cybersecurity program shall include--
(A) the legal justification for the cybersecurity program;
(B) the certification, if any, made pursuant to section 2511(2)(a)(ii)(B) of title 18, United States Code, or other statutory certification of legality for the cybersecurity program;
(C) the concept for the operation of the cybersecurity program that is approved by the head of the appropriate agency or department;
(D) the assessment, if any, of the privacy impact of the cybersecurity program prepared by the privacy or civil liberties protection officer or comparable officer of such agency or department; and
(E) the plan, if any, for independent audit or review of the cybersecurity program to be carried out by the head of the relevant department or agency of the United States, in conjunction with the appropriate inspector general.
(b) Program Reports.--
(1) Requirement for reports.--The head of a department or agency of the United States with responsibility for a cybersecurity program for which a notification was submitted under subsection (a), in consultation with the inspector general for that department or agency, shall submit to Congress and the President, in accordance with the schedule set out in paragraph (2), a report on such cybersecurity program that includes--
(A) the results of any audit or review of the cybersecurity program carried out under the plan referred to in subsection (a)(2)(E), if any; and
(B) an assessment of whether the implementation of the cybersecurity program--
(i) is in compliance with--
(I) the legal justification referred to in subsection (a)(2)(A); and
(II) the assessment referred to in subsection (a)(2)(D), if any;
(ii) is adequately described by the concept of operation referred to in subsection (a)(2)(C), if any; and
(iii) includes an adequate independent audit or review system and whether improvements to such independent audit or review system are necessary.
(2) Schedule for submission of reports.--The reports required by paragraph (1) shall be submitted to Congress and the President according to the following schedule:
(A) An initial report shall be submitted not later than 180 days after the date of the enactment of this Act.
(B) A second report shall be submitted not later than one year after the date of the enactment of this Act.
(C) Additional reports shall be submitted periodically following the submission of the reports referred to in subparagraphs (A) and (B) as necessary, as determined by the head of the relevant department or agency of the United States in conjunction with the inspector general of that department or agency.
(3) Cooperation and coordination.--
(A) Cooperation.--The head of each department or agency of the United States required to submit a report under paragraph (1) for a particular cybersecurity program, and the inspector general of each such department or agency, shall, to the extent practicable, work in conjunction with any other such head or inspector general required to submit such a report for such cybersecurity program.
(B) Coordination.--The heads of all of the departments and agencies of the United States required to submit a report under paragraph (1) for a particular cybersecurity program shall designate one such head to coordinate the conduct of the reports on such program.
(c) Information Sharing Report.--Not later than one year after the date of the enactment of this Act, the Inspector General of the Department of Homeland Security and the Inspector General of the Intelligence Community shall jointly submit to Congress and the President a report on the status of the sharing of cyber threat information, including--
(1) a description of how cyber threat intelligence information, including classified information, is shared among the agencies and departments of the United States and with persons responsible for critical infrastructure;
(2) a description of the mechanisms by which classified cyber threat information is distributed;
(3) an assessment of the effectiveness of such information sharing and distribution; and
(4) any other matters identified by the Inspectors General that would help to fully inform Congress or the President regarding the effectiveness and legality of cybersecurity programs.
(d) Personnel Details.--
(1) Authority to detail.--Notwithstanding any other provision of law, the head of an element of the intelligence community that is funded through the National Intelligence Program may detail an officer or employee of such element to the National Cyber Investigative Joint Task Force or to the Department of Homeland Security to assist the Task Force or the Department with cybersecurity, as jointly agreed by the head of such element and the Task Force or the Department.
(2) Basis for detail.--A personnel detail made under paragraph (1) may be made--
(A) for a period of not more than three years; and
(B) on a reimbursable or nonreimbursable basis.
(e) Sunset.--The requirements and authorities of this section shall terminate on December 31, 2012.
(f) Definitions.--In this section:
(1) Cybersecurity program.--The term “cybersecurity program” means a class or collection of similar cybersecurity operations of an agency or department of the United States that involves personally identifiable data that is--
(A) screened by a cybersecurity system outside of the agency or department of the United States that was the intended recipient of the personally identifiable data;
(B) transferred, for the purpose of cybersecurity, outside the agency or department of the United States that was the intended recipient of the personally identifiable data; or
(C) transferred, for the purpose of cybersecurity, to an element of the intelligence community.
(2) National cyber investigative joint task force.--The term “National Cyber Investigative Joint Task Force” means the multi-agency cyber investigation coordination organization overseen by the Director of the Federal Bureau of Investigation known as the Nation Cyber Investigative Joint Task Force that coordinates, integrates, and provides pertinent information related to cybersecurity investigations.
(3) Critical infrastructure.--The term “critical infrastructure” has the meaning given that term in section 1016 of the USA PATRIOT Act (42 U.S.C. 5195c).
Legislative Activity
Stay on top of the latest movement without scrolling through every action
House amendment offered
February 25, 2010
View full timeline
House amendment offered
February 25, 2010
House amendment agreed to: On agreeing to the Arcuri amendment (A007) Agreed to by voice vote.
February 25, 2010 • 3:41 PM
Amendment agreed to Committee of the Whole
February 25, 2010 • 3:41 PM
House amendment offered/reported by : Amendment (A007) offered by Mr. Arcuri.(consideration: CR H887-888; text: CR H887)
February 25, 2010 • 3:33 PM
Amendment (A007) offered by Mr. Arcuri. (consideration: CR H887-888; text: CR H887)
February 25, 2010 • 3:33 PM
On agreeing to the Arcuri amendment (A007) Agreed to by voice vote.
February 25, 2010 • 3:41 PM