S.Amdt. 2766
What it does: Rewrites page 174, line 12 through page 180, line 14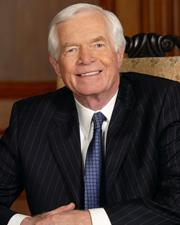 Sen. Thad Cochran (R-MS)
What it changes
1 change to S. 3414
Rewrites page 174, line 12 through page 180, line 14
ReplacesPrinted pageRemoves page 174, line 12 through page 180, line 14 of the printed bill. See that page
Inserted: SEC. 703. CYBERSECURITY EXCHANGES.
Inserted: (a) Designation of Cybersecurity Exchanges.--The Secretary of Homeland Security, in consultation with the Director of National Intelligence, the Attorney General, and the Secretary of Defense, shall establish--
Inserted: (1) a process for designating one or more appropriate civilian Federal entities or non-Federal entities to serve as cybersecurity exchanges to receive and distribute cybersecurity threat indicators;
Inserted: (2) procedures to facilitate and ensure the sharing of classified and unclassified cybersecurity threat indicators in as close to real time as possible with appropriate Federal entities and non-Federal entities in accordance with this title, including through automated and other means that allow for the immediate sharing of such indicators in accordance with this title; and
Inserted: (3) a process for identifying certified entities to receive classified cybersecurity threat indicators in accordance with paragraph (2).
Inserted: (b) Purpose.--The purpose of a cybersecurity exchange is to receive and distribute, in as close to real time as possible, cybersecurity threat indicators in accordance with the requirements of this title and the procedures established under subsection (a)(2), and to thereby avoid unnecessary and duplicative Federal bureaucracy for information sharing as provided in this title.
Inserted: (c) Requirement for a Lead Federal Civilian Cybersecurity Exchange.--
Inserted: (1) In general.--The Secretary, in consultation with the Director of National Intelligence, the Attorney General, and the Secretary of Defense, shall designate a civilian Federal entity as the lead cybersecurity exchange to serve as a focal point within the Federal Government for cybersecurity information sharing among Federal entities and with non-Federal entities.
Inserted: (2) Responsibilities.--The lead Federal civilian cybersecurity exchange designated under paragraph (1) shall--
Inserted: (A) receive and distribute, in as close to real time as possible, cybersecurity threat indicators in accordance with this title and the procedures established under subsection (a)(2);
Inserted: (B) facilitate information sharing, interaction, and collaboration among and between--
Inserted: (i) Federal entities;
Show 23 more inserted paragraphsShow less
Inserted: (ii) State, local, tribal, and territorial governments;
Inserted: (iii) private entities;
Inserted: (iv) academia;
Inserted: (v) international partners, in consultation with the Secretary of State; and
Inserted: (vi) other cybersecurity exchanges;
Inserted: (C) disseminate timely and actionable cybersecurity threat, vulnerability, mitigation, and warning information lawfully obtained from any source, including alerts, advisories, indicators, signatures, and mitigation and response measures, to appropriate Federal and non-Federal entities in accordance with this title and the procedures established under subsection (a)(2) in as close to real time as possible to improve the security and protection of information systems;
Inserted: (D) coordinate with other Federal and non-Federal entities, as appropriate, to integrate information from Federal and non-Federal entities, including Federal cybersecurity centers, non-Federal network or security operation centers, other cybersecurity exchanges, and non-Federal entities that disclose cybersecurity threat indicators under section 704(a), in accordance with this title and the procedures established under subsection (a)(2) in as close to real time as possible, to provide situational awareness of the United States information security posture and foster information security collaboration among information system owners and operators;
Inserted: (E) conduct, in consultation with private entities and relevant Federal and other governmental entities, regular assessments of existing and proposed information sharing models to eliminate bureaucratic obstacles to information sharing and identify best practices for such sharing; and
Inserted: (F) coordinate with other Federal entities, as appropriate, to compile and analyze information about risks and incidents that threaten information systems, including information voluntarily submitted in accordance with section 704(a) or otherwise in accordance with applicable laws.
Inserted: (3) Schedule for designation.--The designation of a lead Federal civilian cybersecurity exchange under paragraph (1) shall be made concurrently with the issuance of the interim policies and procedures under section 704(g)(3)(D).
Inserted: (d) Additional Civilian Federal Cybersecurity Exchanges.--In accordance with the process and procedures established in subsection (a), the Secretary, in consultation with the Director of National Intelligence, the Attorney General, and the Secretary of Defense, may designate additional civilian Federal entities to receive and distribute cybersecurity threat indicators, if such entities are subject to the requirements for use, retention, and disclosure of information by a cybersecurity exchange under section 704(b) and the special requirements for Federal entities under section 704(g).
Inserted: (e) Requirements for Non-Federal Cybersecurity Exchanges.--
Inserted: (1) In general.--In considering whether to designate a private entity or any other non-Federal entity as a cybersecurity exchange to receive and distribute cybersecurity threat indicators under section 704, and what entity to designate, the Secretary shall consider the following factors:
Inserted: (A) The net effect that such designation would have on the overall cybersecurity of the United States.
Inserted: (B) Whether such designation could substantially improve such overall cybersecurity by serving as a hub for receiving and sharing cybersecurity threat indicators in as close to real time as possible, including the capacity of the non-Federal entity for performing those functions in accordance with this title and the procedures established under subsection (a)(2).
Inserted: (C) The capacity of such non-Federal entity to safeguard cybersecurity threat indicators from unauthorized disclosure and use.
Inserted: (D) The adequacy of the policies and procedures of such non-Federal entity to protect personally identifiable information from unauthorized disclosure and use.
Inserted: (E) The ability of the non-Federal entity to sustain operations using entirely non-Federal sources of funding.
Inserted: (2) Regulations.--The Secretary may promulgate regulations as may be necessary to carry out this subsection.
Inserted: (f) Construction With Other Authorities.--Nothing in this section may be construed to alter the authorities of a Federal cybersecurity center, unless such cybersecurity center is acting in its capacity as a designated cybersecurity exchange.
Inserted: (g) Congressional Notification of Designation of Cybersecurity Exchanges.--
Inserted: (1) In general.--The Secretary, in coordination with the Director of National Intelligence, the Attorney General, and the Secretary of Defense, shall promptly notify Congress, in writing, of any designation of a cybersecurity exchange under this title.
Inserted: (2) Requirement.--Written notification under paragraph (1) shall include a description of the criteria and processes used to make the designation.
Original wording
On page 174, strike line 12 and all that follows through page 180, line 14, and insert the following:
Read automatically from the Congressional Record. Check the original before relying on it.
As printed
SA 2766. Mr. COCHRAN submitted an amendment intended to be proposed by him to the bill S. 3414, to enhance the security and resiliency of the cyber and communications infrastructure of the United States; which was ordered to lie on the table; as follows:
On page 174, strike line 12 and all that follows through page 180, line 14, and insert the following:
SEC. 703. CYBERSECURITY EXCHANGES.
(a) Designation of Cybersecurity Exchanges.--The Secretary of Homeland Security, in consultation with the Director of National Intelligence, the Attorney General, and the Secretary of Defense, shall establish--
(1) a process for designating one or more appropriate civilian Federal entities or non-Federal entities to serve as cybersecurity exchanges to receive and distribute cybersecurity threat indicators;
(2) procedures to facilitate and ensure the sharing of classified and unclassified cybersecurity threat indicators in as close to real time as possible with appropriate Federal entities and non-Federal entities in accordance with this title, including through automated and other means that allow for the immediate sharing of such indicators in accordance with this title; and
(3) a process for identifying certified entities to receive classified cybersecurity threat indicators in accordance with paragraph (2).
(b) Purpose.--The purpose of a cybersecurity exchange is to receive and distribute, in as close to real time as possible, cybersecurity threat indicators in accordance with the requirements of this title and the procedures established under subsection (a)(2), and to thereby avoid unnecessary and duplicative Federal bureaucracy for information sharing as provided in this title.
(c) Requirement for a Lead Federal Civilian Cybersecurity Exchange.--
(1) In general.--The Secretary, in consultation with the Director of National Intelligence, the Attorney General, and the Secretary of Defense, shall designate a civilian Federal entity as the lead cybersecurity exchange to serve as a focal point within the Federal Government for cybersecurity information sharing among Federal entities and with non-Federal entities.
(2) Responsibilities.--The lead Federal civilian cybersecurity exchange designated under paragraph (1) shall--
(A) receive and distribute, in as close to real time as possible, cybersecurity threat indicators in accordance with this title and the procedures established under subsection (a)(2);
(B) facilitate information sharing, interaction, and collaboration among and between--
(i) Federal entities;
(ii) State, local, tribal, and territorial governments;
(iii) private entities;
(iv) academia;
(v) international partners, in consultation with the Secretary of State; and
(vi) other cybersecurity exchanges;
(C) disseminate timely and actionable cybersecurity threat, vulnerability, mitigation, and warning information lawfully obtained from any source, including alerts, advisories, indicators, signatures, and mitigation and response measures, to appropriate Federal and non-Federal entities in accordance with this title and the procedures established under subsection (a)(2) in as close to real time as possible to improve the security and protection of information systems;
(D) coordinate with other Federal and non-Federal entities, as appropriate, to integrate information from Federal and non-Federal entities, including Federal cybersecurity centers, non-Federal network or security operation centers, other cybersecurity exchanges, and non-Federal entities that disclose cybersecurity threat indicators under section 704(a), in accordance with this title and the procedures established under subsection (a)(2) in as close to real time as possible, to provide situational awareness of the United States information security posture and foster information security collaboration among information system owners and operators;
(E) conduct, in consultation with private entities and relevant Federal and other governmental entities, regular assessments of existing and proposed information sharing models to eliminate bureaucratic obstacles to information sharing and identify best practices for such sharing; and
(F) coordinate with other Federal entities, as appropriate, to compile and analyze information about risks and incidents that threaten information systems, including information voluntarily submitted in accordance with section 704(a) or otherwise in accordance with applicable laws.
(3) Schedule for designation.--The designation of a lead Federal civilian cybersecurity exchange under paragraph (1) shall be made concurrently with the issuance of the interim policies and procedures under section 704(g)(3)(D).
(d) Additional Civilian Federal Cybersecurity Exchanges.--In accordance with the process and procedures established in subsection (a), the Secretary, in consultation with the Director of National Intelligence, the Attorney General, and the Secretary of Defense, may designate additional civilian Federal entities to receive and distribute cybersecurity threat indicators, if such entities are subject to the requirements for use, retention, and disclosure of information by a cybersecurity exchange under section 704(b) and the special requirements for Federal entities under section 704(g).
(e) Requirements for Non-Federal Cybersecurity Exchanges.--
(1) In general.--In considering whether to designate a private entity or any other non-Federal entity as a cybersecurity exchange to receive and distribute cybersecurity threat indicators under section 704, and what entity to designate, the Secretary shall consider the following factors:
(A) The net effect that such designation would have on the overall cybersecurity of the United States.
(B) Whether such designation could substantially improve such overall cybersecurity by serving as a hub for receiving and sharing cybersecurity threat indicators in as close to real time as possible, including the capacity of the non-Federal entity for performing those functions in accordance with this title and the procedures established under subsection (a)(2).
(C) The capacity of such non-Federal entity to safeguard cybersecurity threat indicators from unauthorized disclosure and use.
(D) The adequacy of the policies and procedures of such non-Federal entity to protect personally identifiable information from unauthorized disclosure and use.
(E) The ability of the non-Federal entity to sustain operations using entirely non-Federal sources of funding.
(2) Regulations.--The Secretary may promulgate regulations as may be necessary to carry out this subsection.
(f) Construction With Other Authorities.--Nothing in this section may be construed to alter the authorities of a Federal cybersecurity center, unless such cybersecurity center is acting in its capacity as a designated cybersecurity exchange.
(g) Congressional Notification of Designation of Cybersecurity Exchanges.--
(1) In general.--The Secretary, in coordination with the Director of National Intelligence, the Attorney General, and the Secretary of Defense, shall promptly notify Congress, in writing, of any designation of a cybersecurity exchange under this title.
(2) Requirement.--Written notification under paragraph (1) shall include a description of the criteria and processes used to make the designation.
Legislative Activity
Stay on top of the latest movement without scrolling through every action
Senate amendment submitted
August 1, 2012